Mostrando entradas con la etiqueta Bibliografia. Mostrar todas las entradas

domingo, 10 de abril de 2022

Nueva version de guia NIST: Enterprise Patch Management Planning: Preventive Maintenance for Technology

El Instituto Nacional de Estándares y Tecnología (NIST) de los Estados Unidos ha publicado Special Publication (SP) 800-40 Revision 4, Guide to Enterprise Patch Management Planning: Preventive Maintenance for Technology y SP 1800-31, Improving Enterprise Patching for General IT Systems: Utilizing Existing Tools and Performing Processes in Better Ways.

La administración de parches empresariales es el proceso de identificar, priorizar, adquirir, instalar y verificar la instalación de parches, actualizaciones y mejoras en toda una organización. 

La aplicación de parches es un componente crítico del mantenimiento preventivo de las tecnologías informáticas. Es más importante que nunca debido a la creciente dependencia de la tecnología, ayudando a prevenir compromisos, violaciones de datos, interrupciones operativas y otros eventos adversos. Sin embargo, a menudo existe una división entre los propietarios de la misión/negocio de una organización y la gestión de seguridad/tecnología sobre el valor y la oportunidad de la aplicación de parches.

Report Number: 800-40r4
NIST Pub Series Special Publication (NIST SP)
Pub Type NIST Pubs


Keywords
enterprise patch management, patch, risk management, update, upgrade, vulnerability management.





miércoles, 26 de enero de 2022

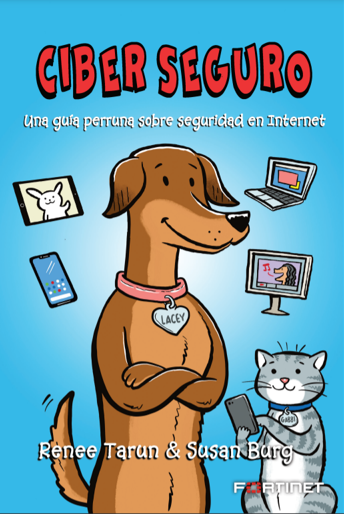
Libro digital "Ciber Seguro" para niños


"Ciber Seguro" es una forma divertida de garantizar que los niños comprendan su entorno en nuestro mundo digital mientras se unen a Lacey y Gabbi en una aventura divertida y cibersegura para aprender a comportarse y mantenerse seguros en línea. 

Sobre las autoras 
Renee Tarun es una mamá con más de 20 años de experiencia en ciberseguridad. Es la subdirectora de Seguridad de la Información (CISO) en Fortinet; antes de eso, trabajó en la Agencia de Seguridad Nacional (NSA) de Estados Unidos. 

 Susan Burg es una maestra certificada por la Junta Nacional con 24 años de experiencia en docencia. Le encantan los niños y le encanta escribir; actualmente, está trabajando en una serie de novelas juveniles sobre una niña llamada Gracie.


sábado, 27 de noviembre de 2021

Los 8 mejores libros de seguridad cibernética, recomendados por los expertos

Los buenos libros de seguridad cibernética comparten ideas obtenidas de situaciones del mundo real y ejemplos de los que podemos aprender como profesionales. Son los grandes los que nos enseñan a qué debemos prestar atención para que estemos preparados para evitar ser víctimas de los ciber delincuentes.


    1. Hackeo: El Arte de la Explotación (2ª Ed.).
    2. El arte de la invisibilidad: el pirata informático más famoso del mundo te enseña a estar seguro en la era de Big Brother y Big Data.
    3. Ghost in the Wires: Mis aventuras como el hacker más buscado del mundo.
    4. The Code Book: La ciencia del secreto del antiguo Egipto a la criptografía cuántica.
    5. Culto de la vaca muerta: cómo el supergrupo de piratería original podría salvar al mundo.
    6. Ingeniería Social: La Ciencia del Pirateo Humano.
    7. Análisis Práctico de Malware.
    8. La guía del CERT sobre las amenazas internas.


    lunes, 30 de noviembre de 2020

    Modelo de madurez en seguridad de AWS


    El workshop publicado permitirá conocer las acciones recomendadas para reforzar su postura de seguridad en cada etapa de su camino hacia la nube.

    La clasificación de las distintas recomendaciones en las categorías depende de la dificultad de implementación del control, el costo de implementación, y el impacto positivo que logrará.

    Se recomienda revisar la introducción e ir avanzando utilizando las flechas > para ir avanzando de página.

    Si ya visitó el modelo y quiere ir directo hacia algún punto, vea el modelo de madurez completo

    El modelo será actualizado semanalmente por lo que se recomienda visitarlo periódicamente.

    https://maturitymodel.security.aws.dev/images/logo-white.png 


    domingo, 27 de septiembre de 2020

    Libro gratuito de "Seguridad del protocolo TLS/SSL. Ataques criptoanalíticos modernos"


    En el dia de hoy se actualizo el libro gratuito de "Seguridad del protocolo TLS/SSL. Ataques criptoanalíticos modernos" con los ataques más famosos publicados hasta septiembre de 2020. 


     Descarga del libro


    miércoles, 10 de junio de 2020

    Ciberseguridad: Capacitaciones gratuitas

    Las siguientes capacitaciones son abiertas a la comunidad y gratuitas .

     ¿Cuál es el objetivo?
    Transmitir buenas prácticas y herramientas para cuidar nuestra privacidad, y la de nuestra familia, en el mundo online.

     Fuente:ba-csirt.gob.ar

    sábado, 23 de mayo de 2020

    Interland es un juego online, al que se puede acceder desde un navegador, y en el que los jugadores deben guiar a una serie de personajes llamados “internauts”, a través de distintos mundos virtuales, en los que deben completar distintas misiones.
    De este modo, en “Reality River”, un mundo en el que los jugadores deben atravesar un río, requiere que los jugadores contesten de manera correcta diez preguntas vinculadas con el modo en el que es posible distinguir información real de otra falsa; ofertas engañosas; y otro tipo de estafas en línea. Cada vez que el jugador responde una pregunta correctamente avanza un casillero. Cuando falla, cae al agua y debe volver a intentarlo.
    En otro mundo llamado “Tower of Treasure”, el estudiante aprende sobre la importancia de proteger sus datos personales, y comienza el nivel adquriendo estrategias para crear contraseñas fuertes y difíciles de violar. Para ello, debe guiar a su personaje a través de un cañón en el que debe recoger distintos bloques compuestos por letras y otros caracteres, y luego combinarlos para formar claves efectivas y seguras.


    miércoles, 15 de abril de 2020

    COVID-19 response: freely available ISO standards

    The below list has been compiled to support global efforts in dealing with the COVID-19 crisis. They are freely available in read-only format.
    • ISO 22301:2019, Security and resilience – Business continuity management systems –Requirements
    • ISO 22395:2018, Security and resilience – Community resilience – Guidelines for supporting vulnerable persons in an emergency
    • ISO 22320:2018, Security and resilience – Emergency management – Guidelines for incident management
    •  ISO 22316:2017, Security and resilience – Organizational resilience – Principles and attributes
    •  ISO 31000:2018, Risk management – Guidelines
    •  More..
    This action has been coordinated with the International Electrotechnical Commission (IEC), who are making complementary standards freely available at go.iec.ch/covid19faq.

    lunes, 9 de marzo de 2020

    Penetration Testing & Hacking Tools List for Hackers & Security Professionals

    Penetration testing & Hacking Tools are more often used by security industries to test the vulnerabilities in network and applications. Here you can find the Comprehensive Penetration testing & Haking Tools list that covers Performing Penetration testing Operation in all the Environment.
    Penetration testing and ethical hacking tools are very essential part for every organization to test the vulnerabilities and patch the vulnerable system


    Penetration Testing & Hacking Tools List
    Online Resources – Hacking Tools

    Penetration Testing Resources

    Exploit Development

    OSINT Resources

    Social Engineering Resources

    Lock Picking Resources

    Operating Systems

    Hacking ToolsPenetration Testing Distributions

    • Kali – GNU/Linux distribution designed for digital forensics and penetration testing Hacking Tools
    • ArchStrike – Arch GNU/Linux repository for security professionals and enthusiasts.
    • BlackArch – Arch GNU/Linux-based distribution with best Hacking Tools for penetration testers and security researchers.
    • Network Security Toolkit (NST) – Fedora-based bootable live operating system designed to provide easy access to best-of-breed open source network security applications.
    • Pentoo – Security-focused live CD based on Gentoo.
    • BackBox – Ubuntu-based distribution for penetration tests and security assessments.
    • Parrot – Distribution similar to Kali, with multiple architectures with 100 of Hacking Tools.
    • Buscador – GNU/Linux virtual machine that is pre-configured for online investigators.
    • Fedora Security Lab – Provides a safe test environment to work on security auditing, forensics, system rescue and teaching security testing methodologies.
    • The Pentesters Framework – Distro organized around the Penetration Testing Execution Standard (PTES), providing a curated collection of utilities that eliminates often unused toolchains.
    • AttifyOS – GNU/Linux distribution focused on tools useful during Internet of Things (IoT) security assessments.

    Docker for Penetration Testing

    Multi-paradigm Frameworks

    • Metasploit – post exploitaion Hacking Tools for offensive security teams to help verify vulnerabilities and manage security assessments.
    • Armitage – Java-based GUI front-end for the Metasploit Framework.
    • Faraday – Multiuser integrated pentesting environment for red teams performing cooperative penetration tests, security audits, and risk assessments.
    • ExploitPack – Graphical tool for automating penetration tests that ships with many pre-packaged exploits.
    • Pupy – Cross-platform (Windows, Linux, macOS, Android) remote administration and post-exploitation tool,

    Vulnerability Scanners

    • Nexpose – Commercial vulnerability and risk management assessment engine that integrates with Metasploit, sold by Rapid7.
    • Nessus – Commercial vulnerability management, configuration, and compliance assessment platform, sold by Tenable.
    • OpenVAS – Free software implementation of the popular Nessus vulnerability assessment system.
    • Vuls – Agentless vulnerability scanner for GNU/Linux and FreeBSD, written in Go.

    Static Analyzers

    • Brakeman – Static analysis security vulnerability scanner for Ruby on Rails applications.
    • cppcheck – Extensible C/C++ static analyzer focused on finding bugs.
    • FindBugs – Free software static analyzer to look for bugs in Java code.
    • sobelow – Security-focused static analysis for the Phoenix Framework.
    • bandit – Security oriented static analyser for python code.

    Web Scanners

    • Nikto – Noisy but fast black box web server and web application vulnerability scanner.
    • Arachni – Scriptable framework for evaluating the security of web applications.
    • w3af – Hacking Tools for Web application attack and audit framework.
    • Wapiti – Black box web application vulnerability scanner with built-in fuzzer.
    • SecApps – In-browser web application security testing suite.
    • WebReaver – Commercial, graphical web application vulnerability scanner designed for macOS.
    • WPScan – Hacking Tools of Black box WordPress vulnerability scanner.
    • cms-explorer – Reveal the specific modules, plugins, components and themes that various websites powered by content management systems are running.
    • joomscan – on of the best Hacking Tools for Joomla vulnerability scanner.
    • ACSTIS – Automated client-side template injection (sandbox escape/bypass) detection for AngularJS.

    Network Tools

    • zmap – Open source network scanner that enables researchers to easily perform Internet-wide network studies.
    • nmap – Free security scanner for network exploration & security audits.
    • pig – one of the Hacking Tools forGNU/Linux packet crafting .
    • scanless – Utility for using websites to perform port scans on your behalf so as not to reveal your own IP.
    • tcpdump/libpcap – Common packet analyzer that runs under the command line.
    • Wireshark – Widely-used graphical, cross-platform network protocol analyzer.
    • Network-Tools.com – Website offering an interface to numerous basic network utilities like ping, traceroute, whois, and more.
    • netsniff-ng – Swiss army knife for for network sniffing.
    • Intercepter-NG – Multifunctional network toolkit.
    • SPARTA – Graphical interface offering scriptable, configurable access to existing network infrastructure scanning and enumeration tools.
    • dnschef – Highly configurable DNS proxy for pentesters.
    • DNSDumpster – one of the Hacking Tools for Online DNS recon and search service.
    • CloudFail – Unmask server IP addresses hidden behind Cloudflare by searching old database records and detecting misconfigured DNS.
    • dnsenum – Perl script that enumerates DNS information from a domain, attempts zone transfers, performs a brute force dictionary style attack, and then performs reverse look-ups on the results.
    • dnsmap – One of the Hacking Tools for Passive DNS network mapper.
    • dnsrecon – One of the Hacking Tools for DNS enumeration script.
    • dnstracer – Determines where a given DNS server gets its information from, and follows the chain of DNS servers.
    • passivedns-client – Library and query tool for querying several passive DNS providers.
    • passivedns – Network sniffer that logs all DNS server replies for use in a passive DNS setup.
    • Mass Scan – best Hacking Tools for TCP port scanner, spews SYN packets asynchronously, scanning entire Internet in under 5 minutes.
    • Zarp – Network attack tool centered around the exploitation of local networks.
    • mitmproxy – Interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
    • Morpheus – Automated ettercap TCP/IP Hacking Tools .
    • mallory – HTTP/HTTPS proxy over SSH.
    • SSH MITM – Intercept SSH connections with a proxy; all plaintext passwords and sessions are logged to disk.
    • Netzob – Reverse engineering, traffic generation and fuzzing of communication protocols.
    • DET – Proof of concept to perform data exfiltration using either single or multiple channel(s) at the same time.
    • pwnat – Punches holes in firewalls and NATs.
    • dsniff – Collection of tools for network auditing and pentesting.
    • tgcd – Simple Unix network utility to extend the accessibility of TCP/IP based network services beyond firewalls.
    • smbmap – Handy SMB enumeration tool.
    • scapy – Python-based interactive packet manipulation program & library.
    • Dshell – Network forensic analysis framework.
    • Debookee – Simple and powerful network traffic analyzer for macOS.
    • Dripcap – Caffeinated packet analyzer.
    • Printer Exploitation Toolkit (PRET) – Tool for printer security testing capable of IP and USB connectivity, fuzzing, and exploitation of PostScript, PJL, and PCL printer language features.
    • Praeda – Automated multi-function printer data harvester for gathering usable data during security assessments.
    • routersploit – Open source exploitation framework similar to Metasploit but dedicated to embedded devices.
    • evilgrade – Modular framework to take advantage of poor upgrade implementations by injecting fake updates.
    • XRay – Network (sub)domain discovery and reconnaissance automation tool.
    • Ettercap – Comprehensive, mature suite for machine-in-the-middle attacks.
    • BetterCAP – Modular, portable and easily extensible MITM framework.
    • CrackMapExec – A swiss army knife for pentesting networks.
    • impacket – A collection of Python classes for working with network protocols.

    Wireless Network Hacking Tools

    • Aircrack-ng – Set of Penetration testing & Hacking Tools list for auditing wireless networks.
    • Kismet – Wireless network detector, sniffer, and IDS.
    • Reaver – Brute force attack against WiFi Protected Setup.
    • Wifite – Automated wireless attack tool.
    • Fluxion – Suite of automated social engineering based WPA attacks.

    Transport Layer Security Tools

    • SSLyze – Fast and comprehensive TLS/SSL configuration analyzer to help identify security mis-configurations.
    • tls_prober – Fingerprint a server’s SSL/TLS implementation.
    • testssl.sh – Command line tool which checks a server’s service on any port for the support of TLS/SSL ciphers, protocols as well as some cryptographic flaws.

    Web Exploitation

    • OWASP Zed Attack Proxy (ZAP) – Feature-rich, scriptable HTTP intercepting proxy and fuzzer for penetration testing web applications.
    • Fiddler – Free cross-platform web debugging proxy with user-friendly companion tools.
    • Burp Suite – One of the Hacking Tools ntegrated platform for performing security testing of web applications.
    • autochrome – Easy to install a test browser with all the appropriate setting needed for web application testing with native Burp support, from NCCGroup.
    • Browser Exploitation Framework (BeEF) – Command and control server for delivering exploits to commandeered Web browsers.
    • Offensive Web Testing Framework (OWTF) – Python-based framework for pentesting Web applications based on the OWASP Testing Guide.
    • WordPress Exploit Framework – Ruby framework for developing and using modules which aid in the penetration testing of WordPress powered websites and systems.
    • WPSploit – Exploit WordPress-powered websites with Metasploit.
    • SQLmap – Automatic SQL injection and database takeover tool.
    • tplmap – Automatic server-side template injection and Web server takeover Hacking Tools .
    • weevely3 – Weaponized web shell.
    • Wappalyzer – Wappalyzer uncovers the technologies used on websites.
    • WhatWeb – Website fingerprinter.
    • BlindElephant – Web application fingerprinter.
    • wafw00f – Identifies and fingerprints Web Application Firewall (WAF) products.
    • fimap – Find, prepare, audit, exploit and even Google automatically for LFI/RFI bugs.
    • Kadabra – Automatic LFI exploiter and scanner.
    • Kadimus – LFI scan and exploit tool.
    • liffy – LFI exploitation tool.
    • Commix – Automated all-in-one operating system command injection and exploitation tool.
    • DVCS Ripper – Rip web accessible (distributed) version control systems: SVN/GIT/HG/BZR.
    • GitTools – One of the Hacking Tools that Automatically find and download Web-accessible .git repositories.
    • sslstrip –
      One of the Hacking Tools Demonstration of the HTTPS stripping attacks.
    • sslstrip2 – SSLStrip version to defeat HSTS.
    • NoSQLmap – Automatic NoSQL injection and database takeover tool.
    • VHostScan – A virtual host scanner that performs reverse lookups, can be used with pivot tools, detect catch-all scenarios, aliases and dynamic default pages.
    • FuzzDB – Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
    • EyeWitness – Tool to take screenshots of websites, provide some server header info, and identify default credentials if possible.
    • webscreenshot – A simple script to take screenshots of list of websites.

    Hex Editors

    • HexEdit.js – Browser-based hex editing.
    • Hexinator – World’s finest (proprietary, commercial) Hex Editor.
    • Frhed – Binary file editor for Windows.
    • 0xED – Native macOS hex editor that supports plug-ins to display custom data types.

    File Format Analysis Tools

    • Kaitai Struct – File formats and network protocols dissection language and web IDE, generating parsers in C++, C#, Java, JavaScript, Perl, PHP, Python, Ruby.
    • Veles – Binary data visualization and analysis tool.
    • Hachoir – Python library to view and edit a binary stream as tree of fields and tools for metadata extraction.

    Defense Evasion Tools

    • Veil – Generate metasploit payloads that bypass common anti-virus solutions.
    • shellsploit – Generates custom shellcode, backdoors, injectors, optionally obfuscates every byte via encoders.
    • Hyperion – Runtime encryptor for 32-bit portable executables (“PE .exes”).
    • AntiVirus Evasion Tool (AVET) – Post-process exploits containing executable files targeted for Windows machines to avoid being recognized by antivirus software.
    • peCloak.py – Automates the process of hiding a malicious Windows executable from antivirus (AV) detection.
    • peCloakCapstone – Multi-platform fork of the peCloak.py automated malware antivirus evasion tool.
    • UniByAv – Simple obfuscator that takes raw shellcode and generates Anti-Virus friendly executables by using a brute-forcable, 32-bit XOR key.

    Hash Cracking Hacking Tools

    • John the Ripper – One of the best Hacking Tools for Fast password cracker.
    • Hashcat – Another One of the Hacking Tools The more fast hash cracker.
    • CeWL – Generates custom wordlists by spidering a target’s website and collecting unique words.
    • JWT Cracker – Simple HS256 JWT token brute force cracker.
    • Rar Crack – RAR bruteforce cracker.
    • BruteForce Wallet – Find the password of an encrypted wallet file (i.e. wallet.dat).

    Windows Utilities

    • Sysinternals Suite – The Sysinternals Troubleshooting Utilities.
    • Windows Credentials Editor – Inspect logon sessions and add, change, list, and delete associated credentials, including Kerberos tickets.
    • mimikatz – Credentials extraction tool for Windows operating system.
    • PowerSploit – PowerShell Post-Exploitation Framework.
    • Windows Exploit Suggester – Detects potential missing patches on the target.
    • Responder – LLMNR, NBT-NS and MDNS poisoner.
    • Bloodhound – Graphical Active Directory trust relationship explorer.
    • Empire – Pure PowerShell post-exploitation agent.
    • Fibratus – Tool for exploration and tracing of the Windows kernel.
    • wePWNise – Generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and exploit mitigation software.
    • redsnarf – Post-exploitation tool for retrieving password hashes and credentials from Windows workstations, servers, and domain controllers.
    • Magic Unicorn – Shellcode generator for numerous attack vectors, including Microsoft Office macros, PowerShell, HTML applications (HTA), or certutil (using fake certificates).
    • DeathStar – Python script that uses Empire’s RESTful API to automate gaining Domain Admin rights in Active Directory environments.

    GNU/Linux Utilities

    macOS Utilities

    • Bella – Pure Python post-exploitation data mining and remote administration tool for macOS.

    DDoS Tools

    • LOIC – Open source network stress tool for Windows.
    • JS LOIC – JavaScript in-browser version of LOIC.
    • SlowLoris – DoS tool that uses low bandwidth on the attacking side.
    • HOIC – Updated version of Low Orbit Ion Cannon, has ‘boosters’ to get around common counter measures.
    • T50 – Faster network stress tool.
    • UFONet – Abuses OSI layer 7 HTTP to create/manage ‘zombies’ and to conduct different attacks using; GET/POST, multithreading, proxies, origin spoofing methods, cache evasion techniques, etc.

    Social Engineering Tools

    • Social Engineer Toolkit (SET) – Open source pentesting framework designed for social engineering featuring a number of custom attack vectors to make believable attacks quickly.
    • King Phisher – One of the Hacking Tools for Phishing campaign toolkit used for creating and managing multiple simultaneous phishing attacks with custom email and server content.
    • Evilginx – MITM attack framework used for phishing credentials and session cookies from any Web service.
    • wifiphisher – Automated phishing attacks against WiFi networks.
    • Catphish – Tool for phishing and corporate espionage written in Ruby.
    • Beelogger – Tool for generating keylooger.

    OSINT Tools

    • Maltego – One of the Hacking Tools and Proprietary software for open source intelligence and forensics, from Paterva.
    • theHarvester – E-mail, subdomain and people names harvester.
    • creepy – Geolocation OSINT tool.
    • metagoofil – Metadata harvester.
    • Google Hacking Database – Database of Google dorks; can be used for recon.
    • Google-dorks – Common Google dorks and others you probably don’t know.
    • GooDork – Command line Google dorking tool.
    • dork-cli – Command line Google dork tool.
    • Censys – Collects data on hosts and websites through daily ZMap and ZGrab scans.
    • Shodan – World’s first search engine for Internet-connected devices.
    • recon-ng – One of the Hacking Tools Full-featured Web Reconnaissance framework written in Python.
    • github-dorks – CLI tool to scan Github repos/organizations for potential sensitive information leak.
    • vcsmap – Plugin-based tool to scan public version control systems for sensitive information.
    • Spiderfoot – Multi-source OSINT automation tool with a Web UI and report visualizations
    • BinGoo – GNU/Linux bash based Bing and Google Dorking Tool.
    • fast-recon – Perform Google dorks against a domain.
    • snitch – Information gathering via dorks.
    • Sn1per – ons of the Hacking Tools for Automated Pentest Recon Scanner.
    • Threat Crowd – Search engine for threats.
    • Virus Total – VirusTotal is a free service that analyzes suspicious files and URLs and facilitates the quick detection of viruses, worms, trojans, and all kinds of malware.
    • DataSploit – OSINT visualizer utilizing Shodan, Censys, Clearbit, EmailHunter, FullContact, and Zoomeye behind the scenes.
    • AQUATONE – Subdomain discovery tool utilizing various open sources producing a report that can be used as input to other tools.
    • Intrigue – Automated OSINT & Attack Surface discovery framework with powerful API, UI and CLI.
    • ZoomEye – Search engine for cyberspace that lets the user find specific network components.

    Anonymity Tools

    • Tor – Free software and onion routed overlay network that helps you defend against traffic analysis.
    • OnionScan – One of the Hacking Tools for investigating the Dark Web by finding operational security issues introduced by Tor hidden service operators.
    • I2P – The Invisible Internet Project.
    • Nipe – Script to redirect all traffic from the machine to the Tor network.
    • What Every Browser Knows About You – Comprehensive detection page to test your own Web browser’s configuration for privacy and identity leaks.

    Reverse Engineering Tools

    • Interactive Disassembler (IDA Pro) – Proprietary multi-processor disassembler and debugger for Windows, GNU/Linux, or macOS; also has a free version, IDA Free.
    • WDK/WinDbg – Windows Driver Kit and WinDbg.
    • OllyDbg – x86 debugger for Windows binaries that emphasizes binary code analysis.
    • Radare2 – Open source, crossplatform reverse engineering framework.
    • x64dbg – Open source x64/x32 debugger for windows.
    • Immunity Debugger – Powerful way to write exploits and analyze malware.
    • Evan’s Debugger – OllyDbg-like debugger for GNU/Linux.
    • Medusa – Open source, cross-platform interactive disassembler.
    • plasma – Interactive disassembler for x86/ARM/MIPS. Generates indented pseudo-code with colored syntax code.
    • peda – Python Exploit Development Assistance for GDB.
    • dnSpy – one of the Hacking Tools to reverse engineer .NET assemblies.
    • binwalk – Fast, easy to use tool for analyzing, reverse engineering, and extracting firmware images.
    • PyREBox – Python scriptable Reverse Engineering sandbox by Cisco-Talos.
    • Voltron – Extensible debugger UI toolkit written in Python.
    • Capstone – Lightweight multi-platform, multi-architecture disassembly framework.
    • rVMI – Debugger on steroids; inspect userspace processes, kernel drivers, and preboot environments in a single tool.
    • Frida – Dynamic instrumentation toolkit for developers, reverse-engineers, and security researchers.

    Physical Access Tools

    • LAN Turtle – Covert “USB Ethernet Adapter” that provides remote access, network intelligence gathering, and MITM capabilities when installed in a local network.
    • USB Rubber Ducky – Customizable keystroke injection attack platform masquerading as a USB thumbdrive.
    • Poisontap – Siphons cookies, exposes internal (LAN-side) router and installs web backdoor on locked computers.
    • WiFi Pineapple – Wireless auditing and penetration testing platform.
    • Proxmark3 – RFID/NFC cloning, replay, and spoofing toolkit often used for analyzing and attacking proximity cards/readers, wireless keys/keyfobs, and more.

    Side-channel Tools

    • ChipWhisperer – Complete open-source toolchain for side-channel power analysis and glitching attacks.

    CTF Tools

    • ctf-tools – Collection of setup scripts to install various security research tools easily and quickly deployable to new machines.
    • Pwntools – Rapid exploit development framework built for use in CTFs.
    • RsaCtfTool – Decrypt data enciphered using weak RSA keys, and recover private keys from public keys using a variety of automated attacks.

    Penetration Testing Report Templates


    Fuente: gbhackers.com